At Daiichi Sankyo, ensuring information security is a fundamental prerequisite for advancing DX through the safe use of data and digital technology. To support the stable supply of pharmaceuticals and the provision of reliable information, we continuously strengthen our measures across both information systems and the control devices and systems at manufacturing sites under a global management framework, to mitigate risks such as information leakage, data tampering, and the disruption of production lines.
Improvement and Strengthening of Global Information Security Management System
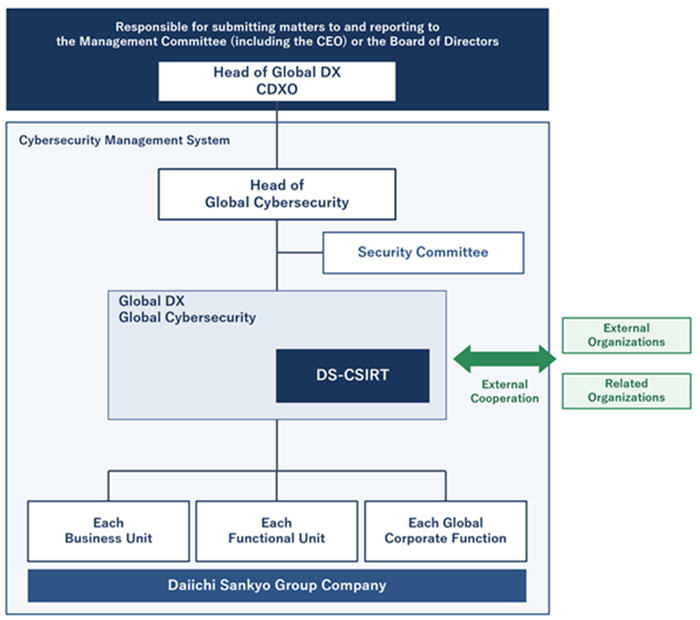
Daiichi Sankyo has established a global policy on information security and designated the CDXO*1 as the officer responsible for information security management. The Head of Global Cybersecurity, appointed by the CDXO, leads information security measures across the entire Daiichi Sankyo Group. This policy covers not only the information and assets held within our Group, but also information entrusted to us by business partners and customers, as well as storage media, information systems, and the control devices and systems involved in the manufacturing and shipment of pharmaceuticals (Operational Technology, or OT). In addition, we have established the Daiichi Sankyo Group Information Security Standards, under which we assess the status of security measures at each Group company and reflect the results in continuous improvement.
Protecting information resources from security threats requires each and every employee to understand the importance of information security and to act appropriately. Daiichi Sankyo continuously provides education on the methods used in cyberattacks, conducts response drills for targeted email attacks, and promotes security awareness among employees.
*1Chief Digital Transformation Officer
Measures for Cyber Security
To respond to cyberattacks, we operate a Computer Security Incident Response Team (CSIRT) under the leadership of the Head of Global Cybersecurity.
We have also implemented an operational platform for our Security Operations Center (SOC), the organization responsible for security monitoring and analysis, to automate log analysis and incident response using AI. In collaboration with external security partners, we maintain 24/7 monitoring and a framework for responding swiftly to incidents.
Responding effectively to cyberattacks requires collaboration that transcends the boundaries of industries and organizations. We share knowledge and information with specialized external organizations and the CSIRTs of other companies and incorporate these insights into the planning and implementation of security measures across the Group. Through such collaboration, we seek to strengthen our own response capabilities while also contributing to the enhancement of cybersecurity across society.
Operational Technology (OT) Security Supporting Manufacturing Sites
To achieve the stable supply of high-quality pharmaceuticals while effectively leveraging digital technology, we are strengthening Operational Technology (OT) security for the control devices and systems involved in pharmaceutical manufacturing processes.
Specifically, we have consolidated recommended security measures for manufacturing sites into standardized security designs and models. We have also designed processes for assessing and managing OT security risks, which are being deployed across our sites. Furthermore, we have established OT-SIRTs (OT Security Incident Response Teams) to respond to incidents involving factory systems and equipment, and conduct exercises based on specific incident scenarios. Through these initiatives, we mitigate risks related to quality control and stable supply, thereby supporting the delivery of pharmaceuticals to patients.
Personal Information Security Initiatives
Personal information is essential to a company's business activities, but by its very nature, may cause irreparable harm to individuals if mishandled. Based on the Daiichi Sankyo Group Global Policy on Privacy, a global standard for protecting personal information, we have established internal rules that comply with the laws and regulations of each country and region to ensure the safe management of personal information. We also regularly conduct training sessions to ensure that all employees are thoroughly trained to handle personal information in the most appropriate manner.
In addition, with regard to handling Individual Numbers in Japan, known informally as “My Number” information, we regularly evaluate the security management status of “My Number” information at our vendors and conduct on-site audits.
In addition, we take appropriate measures such as providing e-learning programs in Japan to ensure that we understand our basic policies and management system.
Moreover, regulations regarding personal information are being enacted around the world, as evidenced by Europe's General Data Protection Regulation (GDPR). We are working to address the personal information protection laws and regulations that will be enforced in the relevant countries and regions.
We will continue to work on reducing risks and identifying issues at an early stage to prevent violations of the personal information protection laws and regulations.